 BUSINESSTECHNOLOGYMicrosoft Ignite 2026: Satya Nadella Puts AI Agents, Copilot and Enterprise Cloud at the Centre of Microsoft's Next Technology RevolutionFlipFileZone · Read Fullopen_in_new
The OpenClaw Meltdown: Uncovering Vulnerabilities and Testing the OWASP Agentic Top 10
A comprehensive real-world test of the OWASP Agentic Top 10 reveals 9 CVEs and 2,200 malicious skills, exposing the OpenClaw meltdown and its implications for cybersecurity
FlipFileZone · TECHNOLOGY
shareShare this post


The OpenClaw Meltdown: Uncovering Vulnerabilities and Testing the OWASP Agentic Top 10
The OpenClaw meltdown has sent shockwaves through the cybersecurity community, with the discovery of 9 CVEs and 2,200 malicious skills. This incident has sparked a thorough examination of the OWASP Agentic Top 10, a widely-recognized standard for web application security.
In this article, we will delve into the details of the OpenClaw meltdown, exploring the vulnerabilities that were exposed and the implications for cybersecurity. We will also discuss the OWASP Agentic Top 10 and its role in preventing similar incidents in the future.
The OpenClaw meltdown is a significant cybersecurity incident that has highlighted the importance of robust security measures. The discovery of 9 CVEs and 2,200 malicious skills has raised concerns about the potential for similar incidents to occur in the future.
The OWASP Agentic Top 10 is a comprehensive guide to web application security, providing a framework for identifying and mitigating potential vulnerabilities. The Top 10 includes a range of categories, from injection and cross-site scripting to security misconfiguration and insufficient logging.
- Injection: The OWASP Agentic Top 10 identifies injection as a major vulnerability, where an attacker can inject malicious code into a web application.
- Cross-Site Scripting (XSS): XSS is another significant vulnerability, where an attacker can inject malicious code into a web page, potentially stealing user data.
- Security Misconfiguration: Security misconfiguration is a common vulnerability, where a web application is not properly configured, leaving it open to attack.
The OpenClaw meltdown has significant implications for cybersecurity, highlighting the need for robust security measures and regular testing. The incident has also raised concerns about the potential for similar incidents to occur in the future, emphasizing the importance of proactive security measures.
In conclusion, the OpenClaw meltdown is a significant cybersecurity incident that has highlighted the importance of robust security measures. The OWASP Agentic Top 10 provides a comprehensive framework for identifying and mitigating potential vulnerabilities, and its importance cannot be overstated.
shareShare this post
recommendYou may also like
BUSINESSTECHNOLOGYMicrosoft Ignite 2026: Satya Nadella Puts AI Agents, Copilot and Enterprise Cloud at the Centre of Microsoft's Next Technology RevolutionFlipFileZone · Read Fullopen_in_new BUSINESSTECHNOLOGYChina Uses American AI Models to Train Domestic Rivals as US Chip Restrictions Intensify the Global Artificial Intelligence RaceFlipFileZone · Read Fullopen_in_new
 BUSINESSTECHNOLOGYNvidia Leadership Turmoil Raises Concerns Over AI Industry Financing as Investors Rethink the Future of the AI BoomFlipFileZone · Read Fullopen_in_new
 TECHNOLOGYGovernor Gulab Chand Kataria launches Shaheed Bhagat Singh Youth Facilitation Centre in LudhianaFlipFileZone · Read Fullopen_in_new
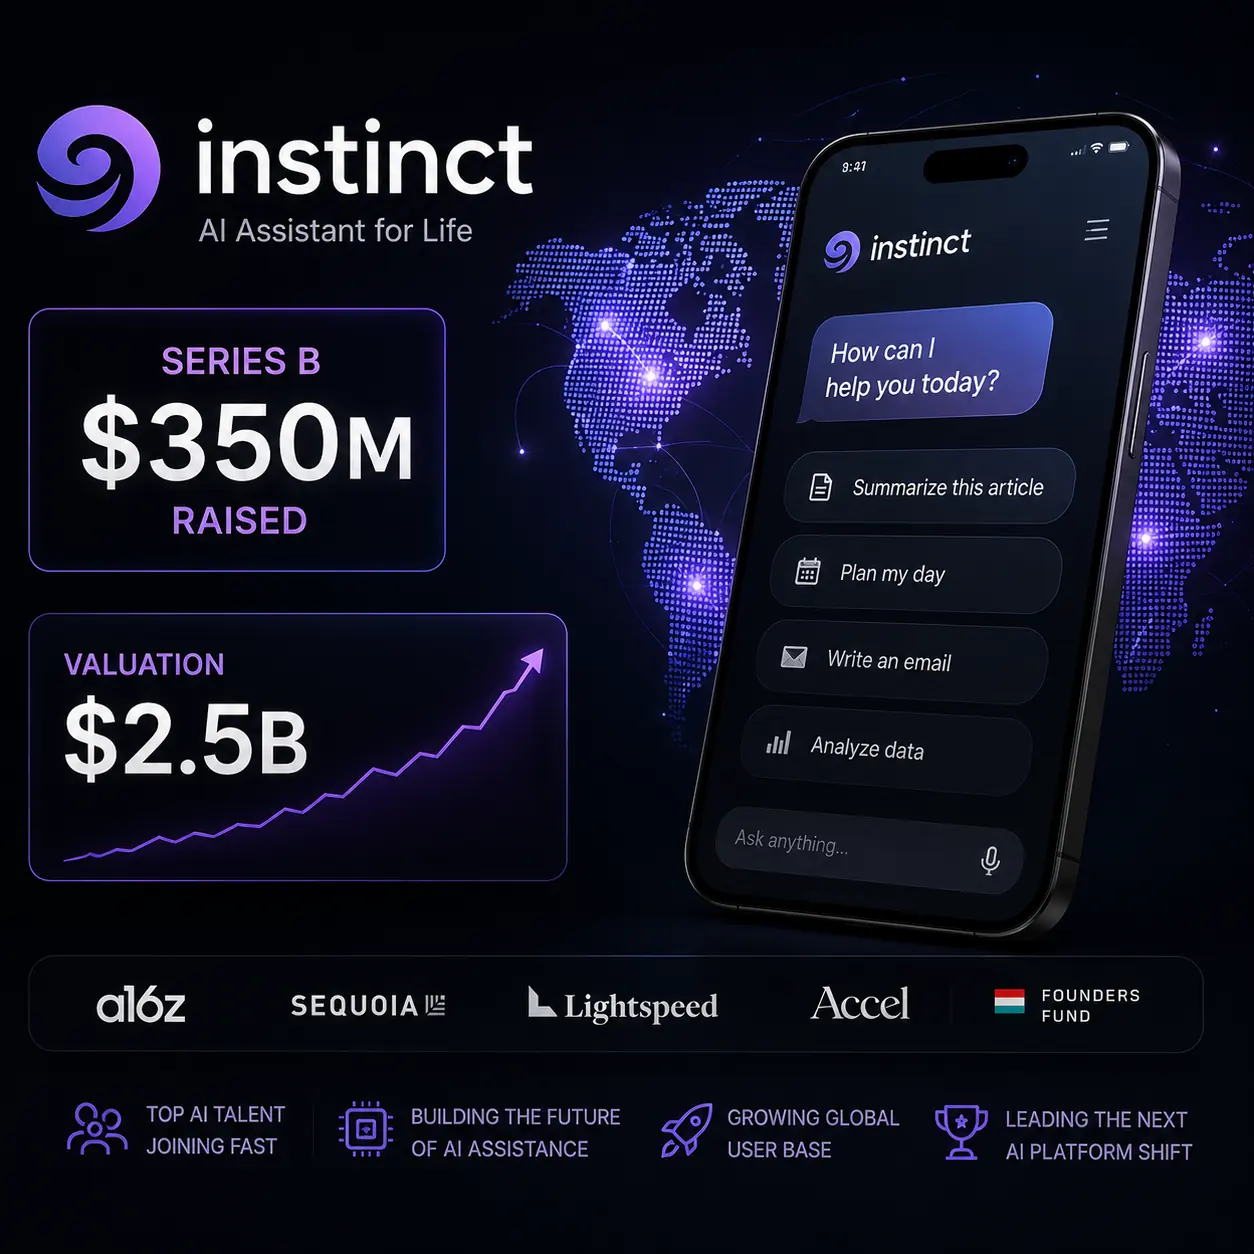 TECHNOLOGYInstinct AI Assistant Secures $350M Funding, Hits $2.5B Valuation in Record TimeFlipFileZone · Read Fullopen_in_new
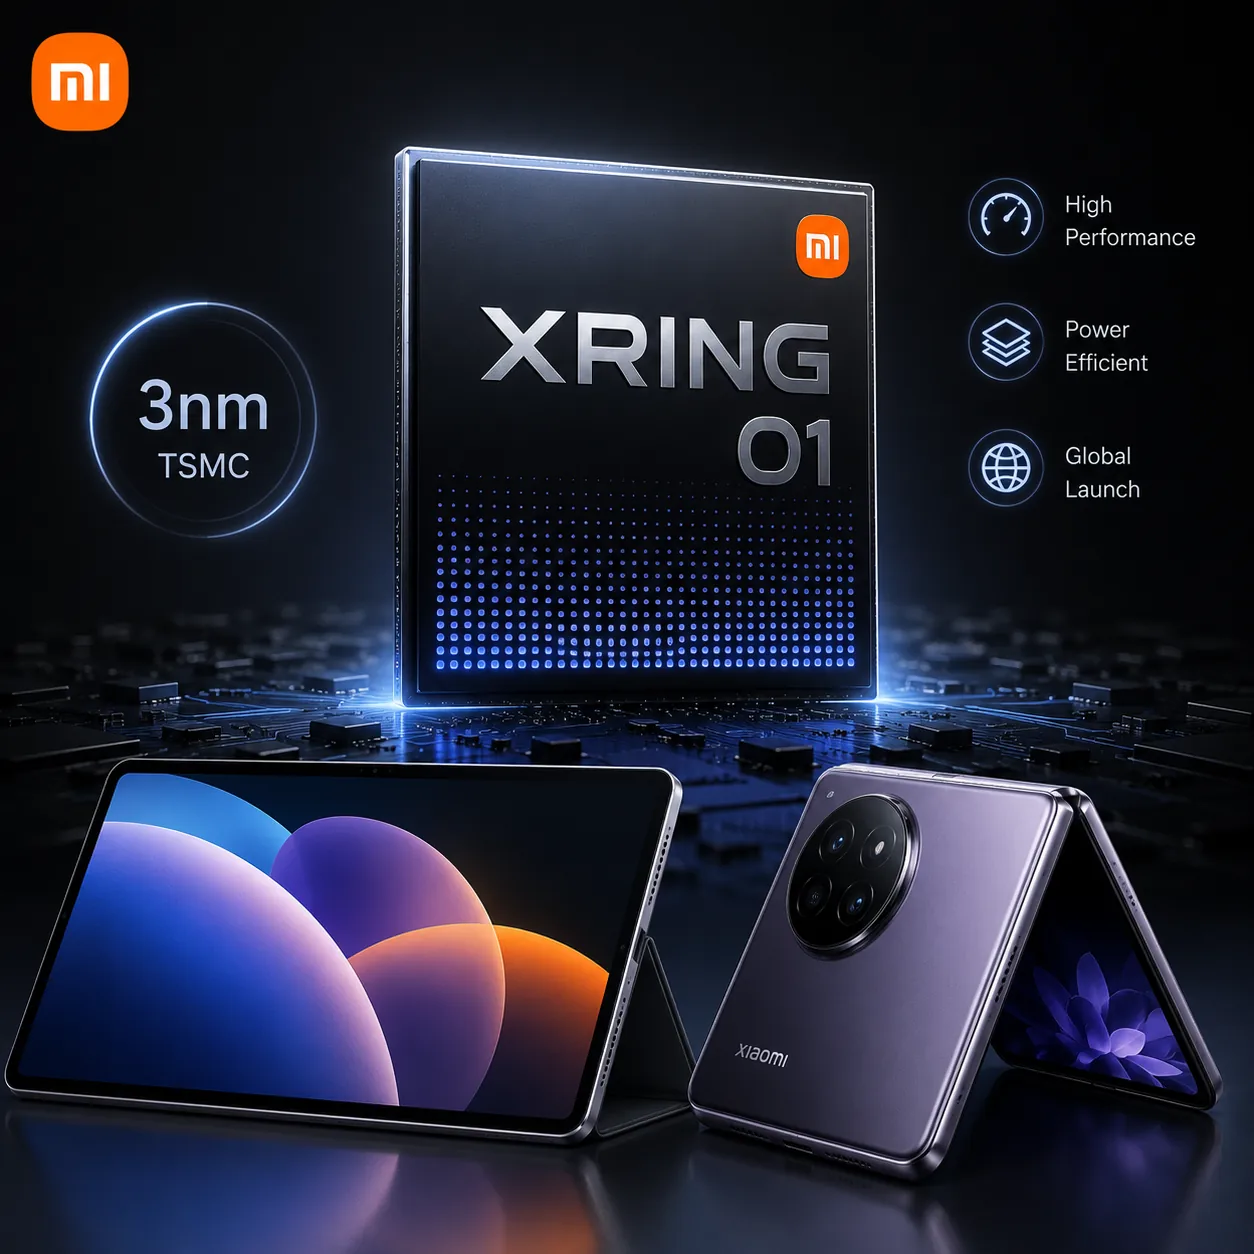 TECHNOLOGYXiaomi Unveils Xring Chip with TSMC Partnership, Redefining Its Global Hardware StrategyFlipFileZone · Read Fullopen_in_new
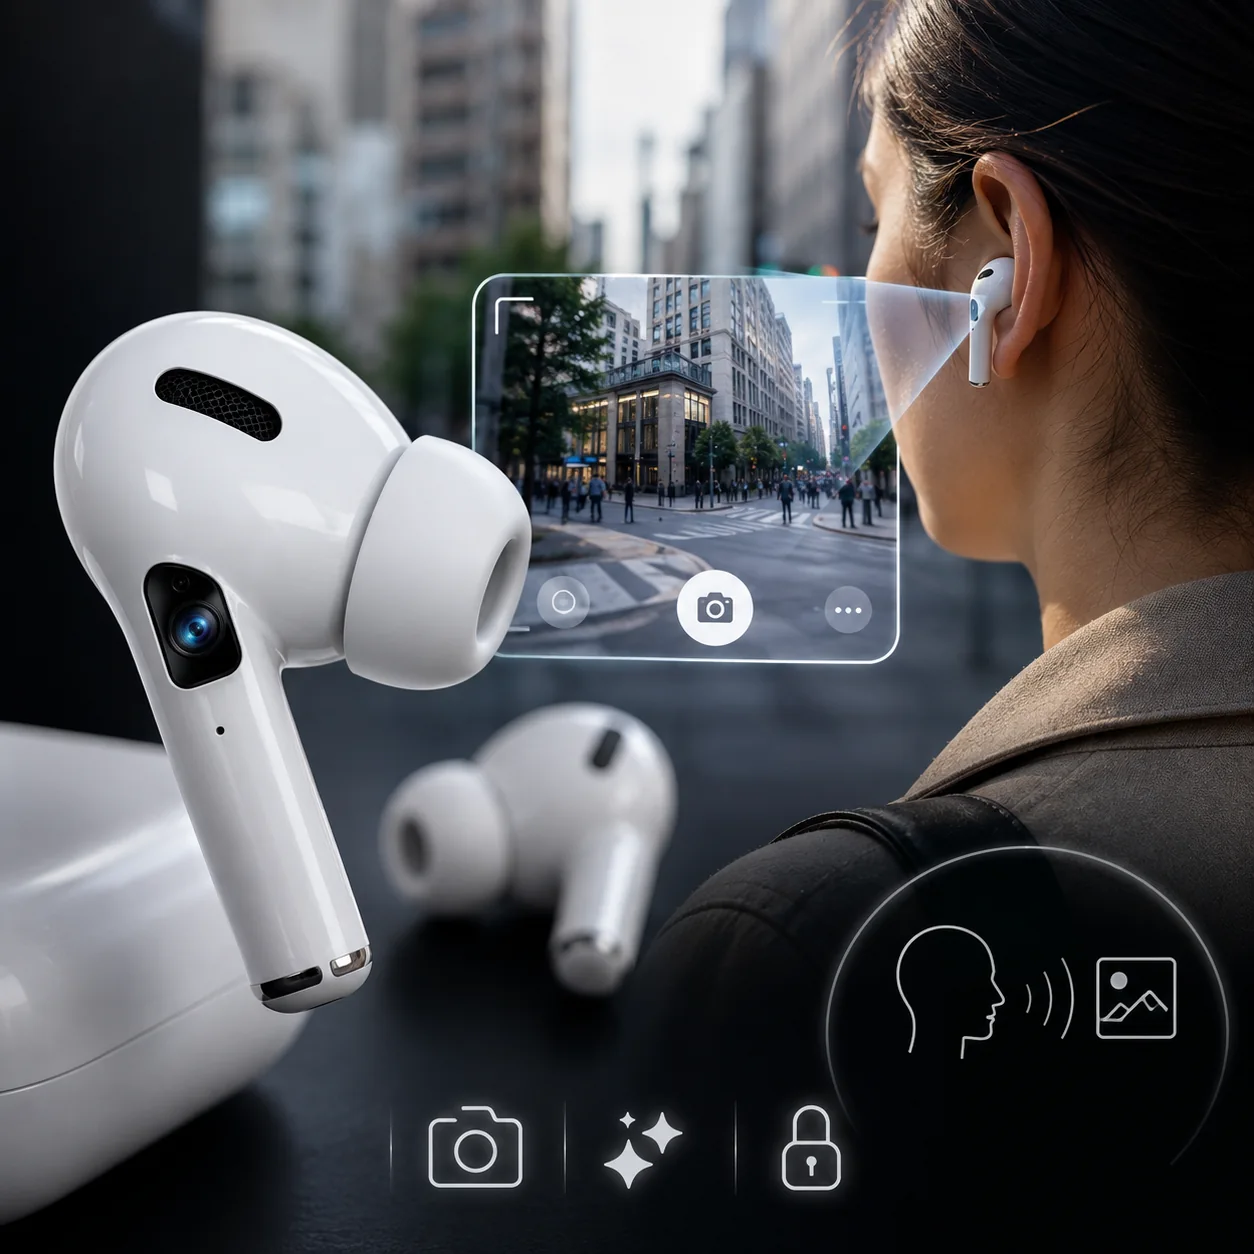 TECHNOLOGYApple’s AI‑Powered Camera AirPods Could Launch in 2026, Not 2027FlipFileZone · Read Fullopen_in_new
chatPost a comment
Comments
0